
 TRUPTI THAKUR
 #CyberSecurity #APISecurity #CERTIn #InformationSecurity #ISO27001 #FinTechSecurity #RiskManagement #DataSecurity #Compliance
Lessons From Cert-In's Latest Warnings
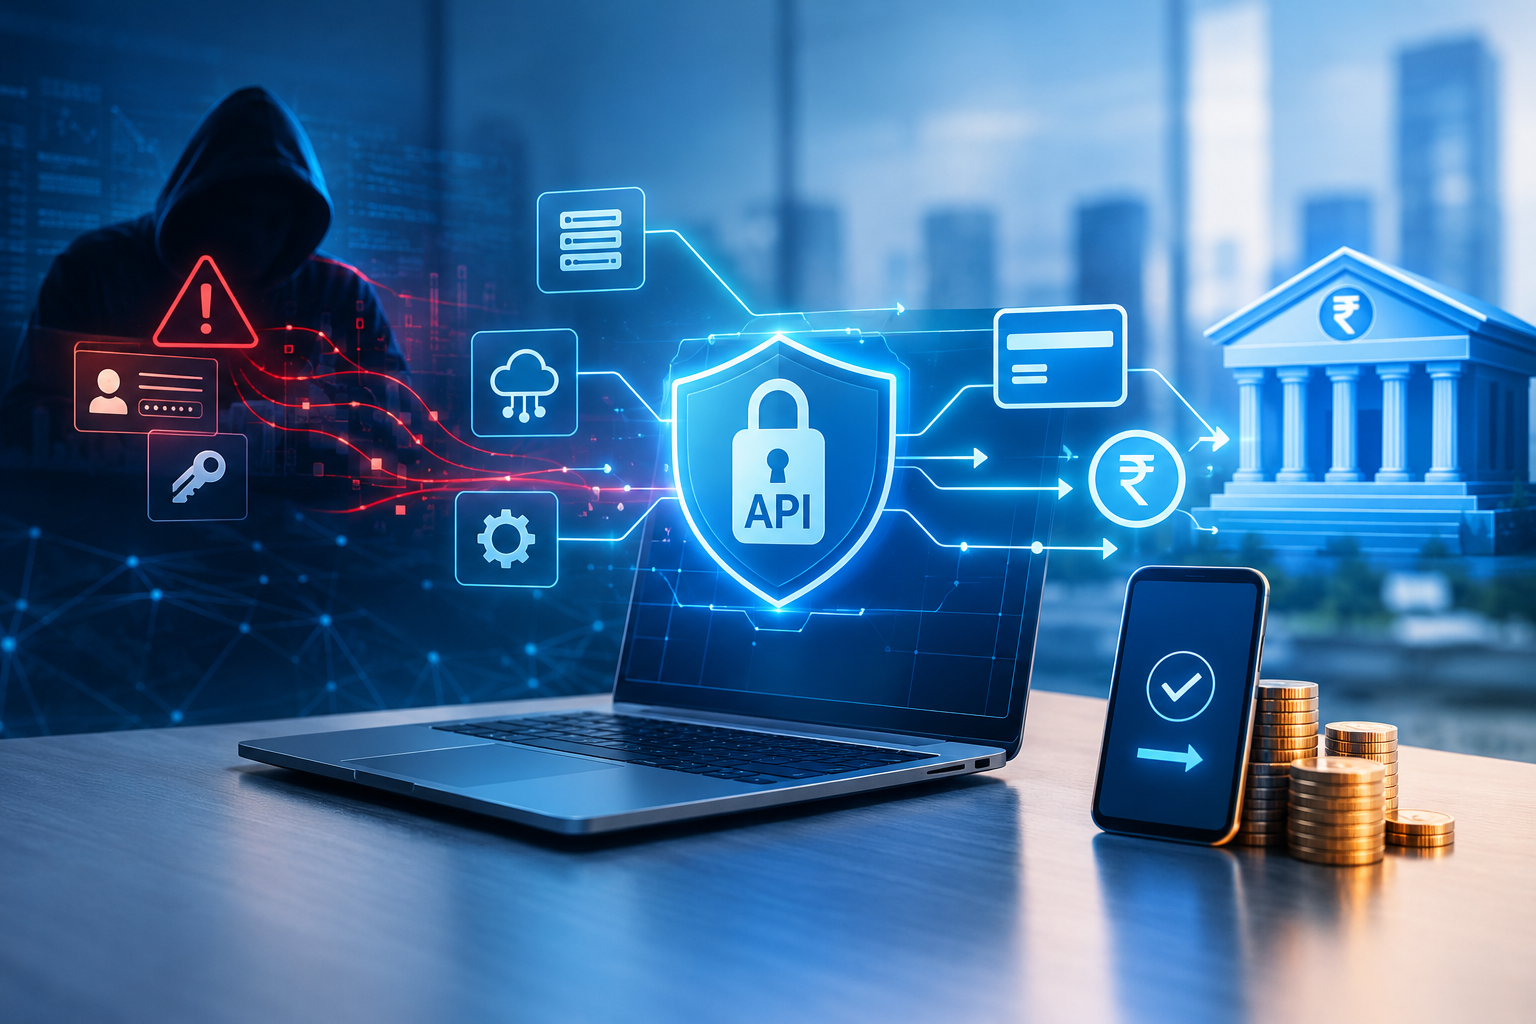
Introduction Application Programming Interfaces (APIs) have become the backbone of modern financial services, enabling digital lending, payment processing, fund transfers, and seamless integration between banking systems. However, as financial institutions increasingly depend on interconnected applications, APIs are also becoming attractive targets for cybercriminals. On 9 October 2026, India’s Computer Emergency Response Team (CERT-In) issued a critical advisory warning about cyberattack campaigns targeting payment and disbursement APIs used by non-banking financial companies (NBFCs), fintech organizations, digital lending platforms, payment service providers, and wallet operators. The advisory highlighted how attackers can exploit exposed applications and compromised API credentials to initiate unauthorized fund transfers while bypassing essential business-level security checks. This development highlights an important security lesson: a system can authenticate a request successfully and still execute a fraudulent transaction. How Are Attackers Exploiting Financial APIs? According to CERT-In, attackers may initially compromise internet-facing applications, exploit vulnerable middleware, misuse outdated or unauthenticated APIs, or obtain credentials stored insecurely in source code and configuration files. Long-lived static API tokens, inadequate multi-factor authentication (MFA), and weaknesses in source-code repositories can further increase exposure. Once access is obtained, attackers may steal payment gateway or partner-bank API credentials and invoke fund-transfer or disbursement endpoints directly from the organization’s own trusted infrastructure. The critical issue is that these requests may appear technically legitimate. However, they can bypass essential business checks, including customer verification, loan approval, beneficiary validation, and transaction limits. Fraudulent transfers may then be directed to attacker-controlled intermediary accounts. CERT-In also highlighted the possible use of AI-assisted offensive tools, alongside the increasing speed between initial compromise and fraudulent fund transfers. These observations demonstrate why organizations must prioritize both preventive security controls and rapid detection mechanisms. Why Traditional Security Controls May Not Be Enough Many organizations rely on firewalls, IP allowlisting, API authentication, and network monitoring to protect financial systems. While these controls remain important, they do not independently establish whether a transaction is legitimate. For example, a payment request originating from an approved server and authenticated using a valid API token may still be fraudulent if the token has been compromised or the request bypasses the required approval workflow. This creates a critical distinction between valid access and authorized business activity. Organizations must therefore validate not only who or what is making an API request, but also whether the requested transaction has a legitimate business purpose, the necessary approvals, a valid reference record, and an eligible beneficiary. Essential Security Measures for Financial Organizations To address these risks, organizations should adopt a layered API security and transaction-governance approach. 1. Strengthen API Authentication and Credential Management Enforce MFA for administrative interfaces and remote access, eliminate unnecessary long-lived static tokens, store credentials in secure secrets-management solutions, and implement controlled credential rotation. Every API should have clearly defined authentication and authorization requirements. 2. Maintain Complete API Visibility Develop and regularly update an API inventory. Identify exposed, deprecated, unused, and unauthenticated endpoints, and formally decommission those that are no longer required. Conduct regular vulnerability assessments and API penetration testing. 3. Validate Transactions at the Payment Layer Do not rely exclusively on application-level checks. Validate every disbursement against approved business records, enforce transaction and daily limits at the payment-processing layer, verify beneficiaries, and reject invalid or unmatched transaction references. 4. Implement Independent Approval Mechanisms Introduce maker-checker controls or second-level verification for fund transfers, particularly high-value or unusual transactions. Critical financial actions should not depend solely on a single compromised application, credential, or automated workflow. 5. Improve Monitoring and Incident Response Monitor transaction patterns, unusual transfer volumes, newly added beneficiaries, suspicious API sequences, and abnormal access behavior. Centralize logs, protect them against unauthorized modification, and establish procedures to suspend affected APIs, revoke compromised credentials, preserve forensic evidence, and report incidents promptly. Connecting API Security with ISO/IEC 27001:2022 Compliance For information security and compliance professionals, this advisory reinforces the importance of translating technical risks into measurable security controls. Organizations implementing ISO/IEC 27001:2022 should evaluate financial API risks within their information security risk assessment, determine appropriate controls through their Statement of Applicability (SoA), and maintain evidence that the selected controls are implemented and effective. Relevant Annex A controls include: • A.5.15 – Access control: Define and enforce appropriate access restrictions. • A.5.18 – Access rights: Review and manage access privileges. • A.8.15 – Logging: Record relevant security events and activities. • A.8.16 – Monitoring activities: Detect anomalous behavior and potential security incidents. • A.8.20 – Network security: Protect networked systems and services. • A.8.25 – Secure development life cycle: Integrate security throughout development. • A.8.29 – Security testing in development and acceptance: Test security requirements before systems are accepted. The applicability of these controls should be determined through the organization's risk assessment and SoA. Compliance should be supported by practical evidence such as API inventories, access reviews, security testing reports, transaction approval records, monitoring alerts, and incident-response exercises. Conclusion CERT-In’s warning demonstrates that API security is no longer just a technical concern for development teams. It is a business-critical responsibility involving information security, finance, risk management, compliance, and senior leadership. As financial services become increasingly automated, organizations must move beyond simply protecting API endpoints. They must verify the legitimacy of every sensitive action, enforce independent transaction approvals, monitor unusual activity, and maintain reliable evidence of control effectiveness. The key question for every organization is no longer just whether its APIs are secure, but whether a compromised API can move money without triggering the controls designed to prevent it. In an increasingly connected financial ecosystem, effective API governance is essential to protecting funds, maintaining customer trust, and strengthening organizational resilience.