
 Trupti Thakur
 #CyberSecurity #InformationSecurity #ZeroTrust #IAM #AI #AIGovernance #CyberRisk #GRC #ISO27001 #IdentitySecurity #CloudSecurity #DigitalTrust
The Trust Gap
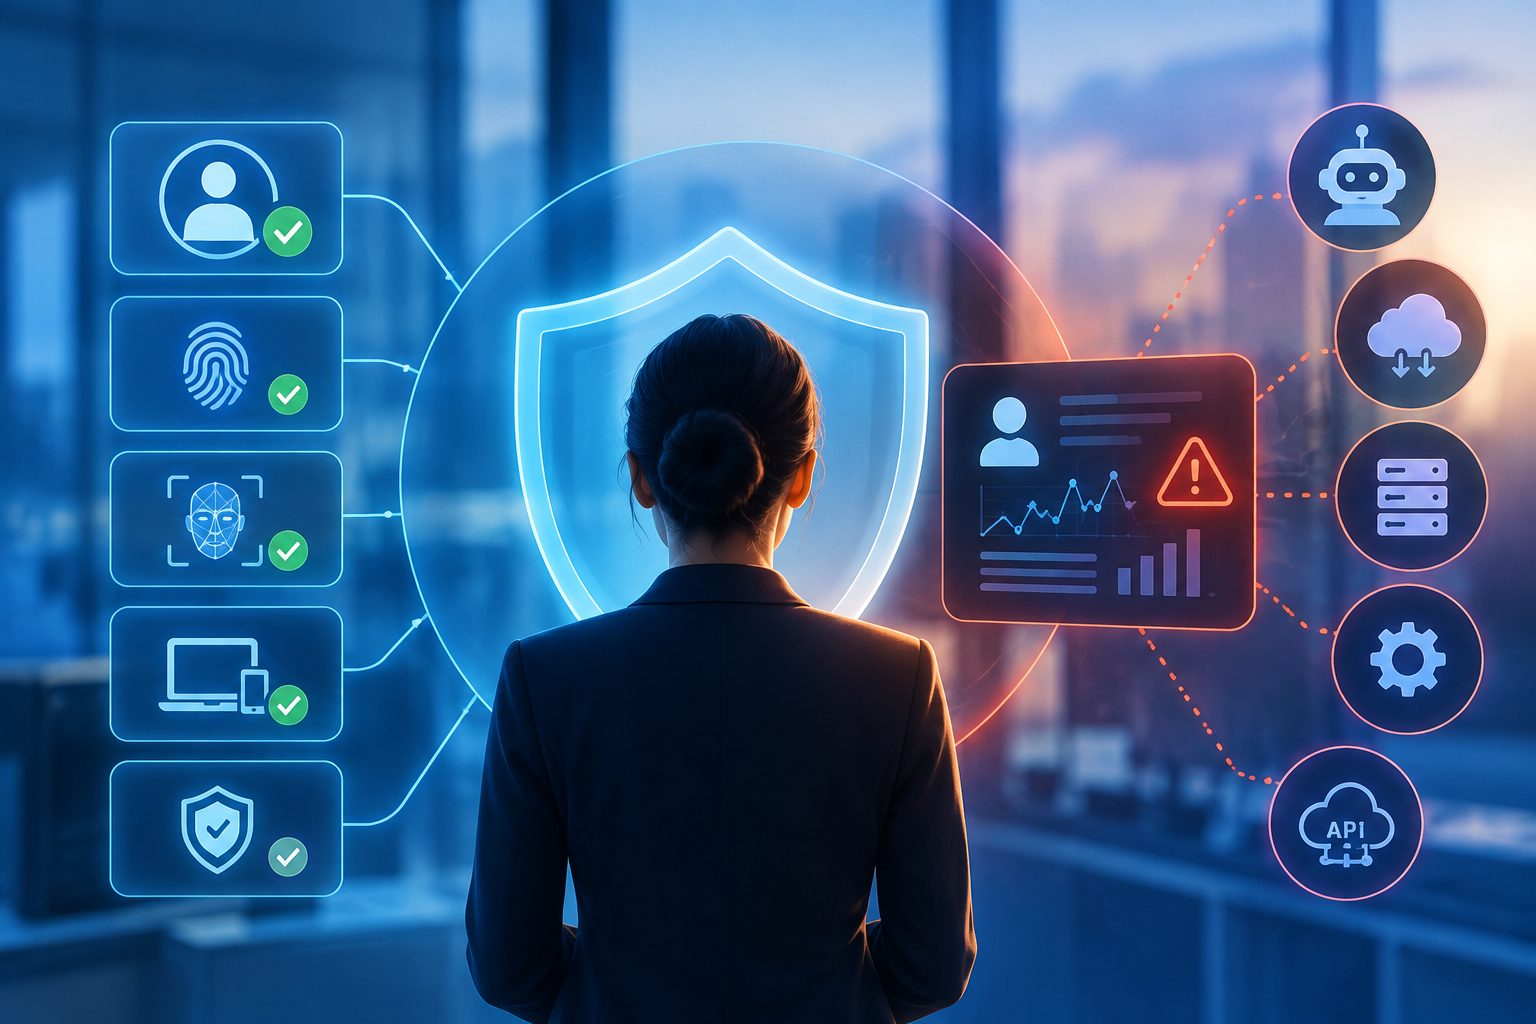
# The Trust Gap: When Systems Can Authenticate You but Cannot Understand You For years, cybersecurity has relied on a fundamental question: **“Who are you?”** Authentication mechanisms, identity providers, passwords, biometrics, certificates, tokens, and multi-factor authentication have become increasingly sophisticated at answering that question. But modern digital environments require us to ask something more important: **“Even if we know who you are, should we trust what you are doing right now?”** This is where the **Trust Gap** emerges. ## Authentication Is Not the Same as Trust A successful authentication confirms that an identity is legitimate. It does not necessarily confirm that the identity's current activity is legitimate. Consider an employee with valid credentials accessing a sensitive database. The authentication succeeds. The account is genuine. The device may even be compliant. But what if the employee suddenly downloads thousands of confidential records at 3:00 AM? The system may recognize the identity perfectly—yet fail to understand that the behavior is abnormal. The same challenge is becoming even more significant with **non-human identities**. Applications, APIs, service accounts, bots, cloud workloads, and AI agents increasingly operate with privileged access. These identities can authenticate successfully and execute authorized actions without a human directly controlling every step. The question is no longer simply **“Is this identity valid?”** It is: **“Is this identity behaving within the trust boundaries we intended?”** ## The Rise of Machine and AI-Driven Trust Modern organizations are moving toward environments where machines interact with machines continuously. An API calls another API. A cloud workload accesses a database. An automated workflow modifies records. An AI agent retrieves information and initiates actions. Each interaction may be technically authorized. However, authorization can become dangerous when permissions remain broader than the actual business requirement or when an identity's behavior changes over time. An AI agent, for example, may legitimately possess access to multiple systems. If its instructions, context, integrations, or underlying model behavior change, the same legitimate permissions could potentially produce unintended consequences. This creates a new security challenge: **A trusted identity can become an untrusted actor without becoming a compromised identity.** ## From Zero Trust to Continuous Trust The principle of **Zero Trust** already challenges the assumption that something should be trusted simply because it is inside the network. But the next evolution is to move beyond continuous verification of identity and device posture toward **continuous evaluation of behavior and intent**. Organizations should increasingly consider: * Is the requested action consistent with the identity's normal behavior? * Is the level of access appropriate for the current activity? * Has the identity suddenly changed its usage pattern? * Is the action consistent with business requirements? * Can the activity be traced to a responsible human or business process? * Can excessive privileges be automatically reduced or revoked? This means identity security, privileged access management, behavioral analytics, data security, and AI governance can no longer operate as completely separate disciplines. ## Closing the Trust Gap Closing the Trust Gap does not mean eliminating trust. It means **making trust conditional, measurable, and continuously evaluated**. Organizations should move toward least privilege, stronger governance of non-human identities, continuous access reviews, behavioral monitoring, segregation of duties, well-defined AI-agent permissions, and clear accountability for automated actions. Most importantly, security teams need to stop treating authentication as the final security decision. Authentication tells us **who—or what—has arrived.** Authorization tells us **what it is allowed to do.** But trust must determine whether **what it is doing makes sense in the context of the organization**. As digital ecosystems become increasingly autonomous, the most dangerous identity may not be the one that has been stolen. It may be the one that is **perfectly legitimate, properly authenticated, fully authorized—and simply trusted too much.**