
 Trupti Thakur
 #CyberSecurity #AI #InformationSecurity #DataSecurity #AIAgents #BehavioralGovernance #ZeroTrust #RiskManagement #CyberRisk #AISecurity #DigitalSecurity
The Behavioral Governance
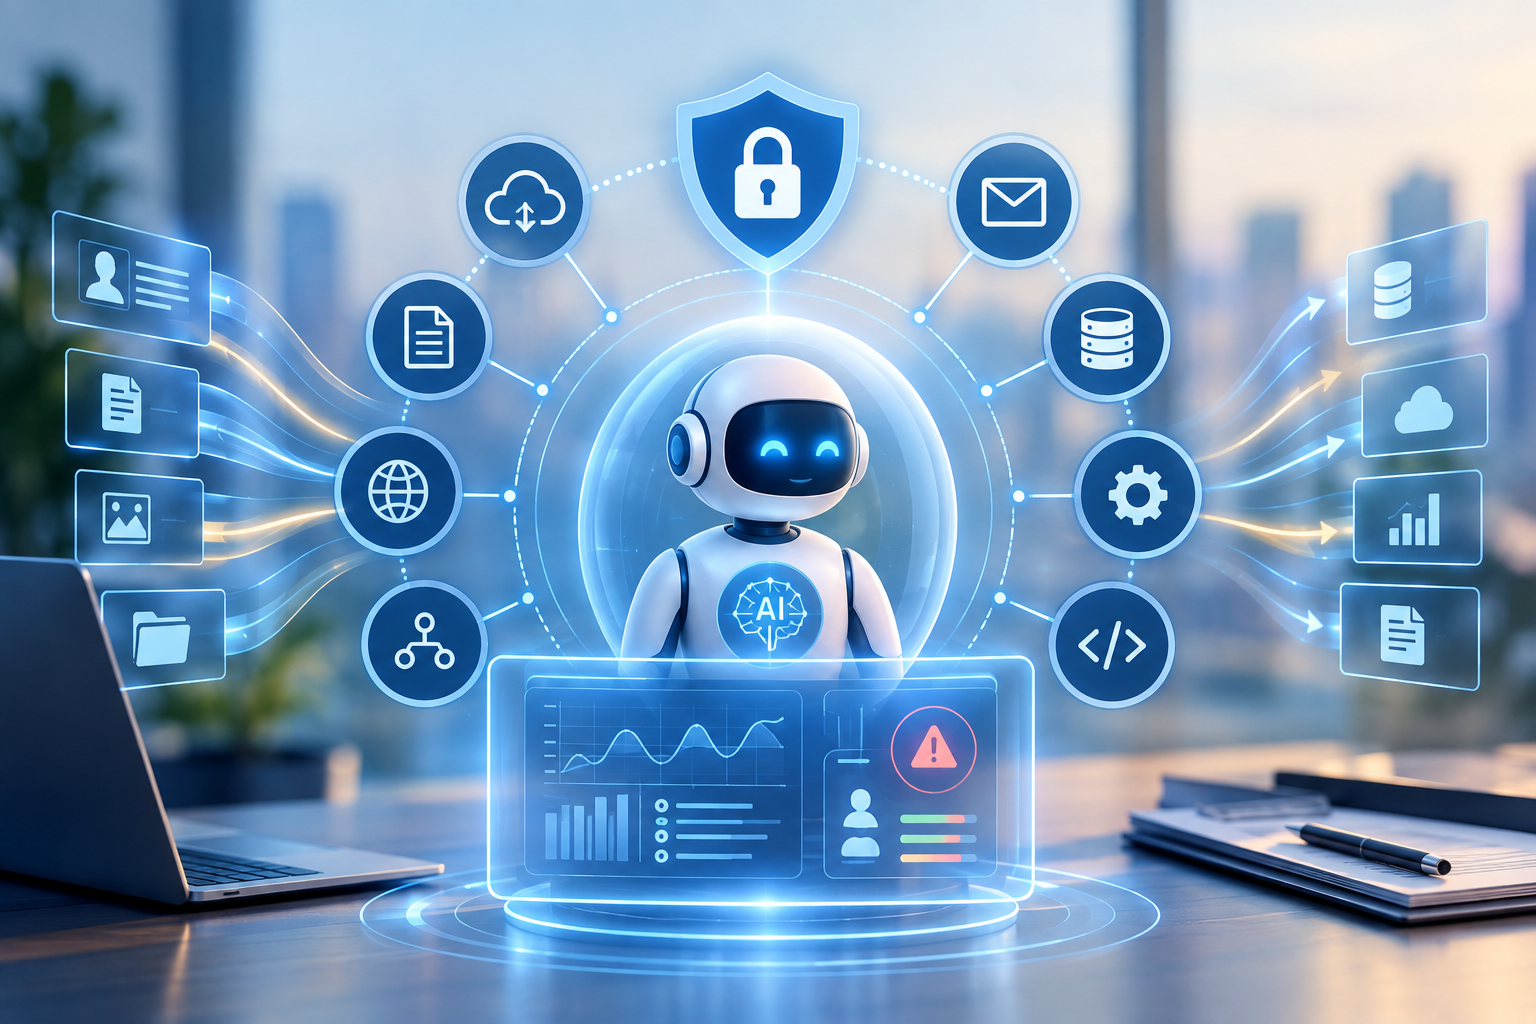
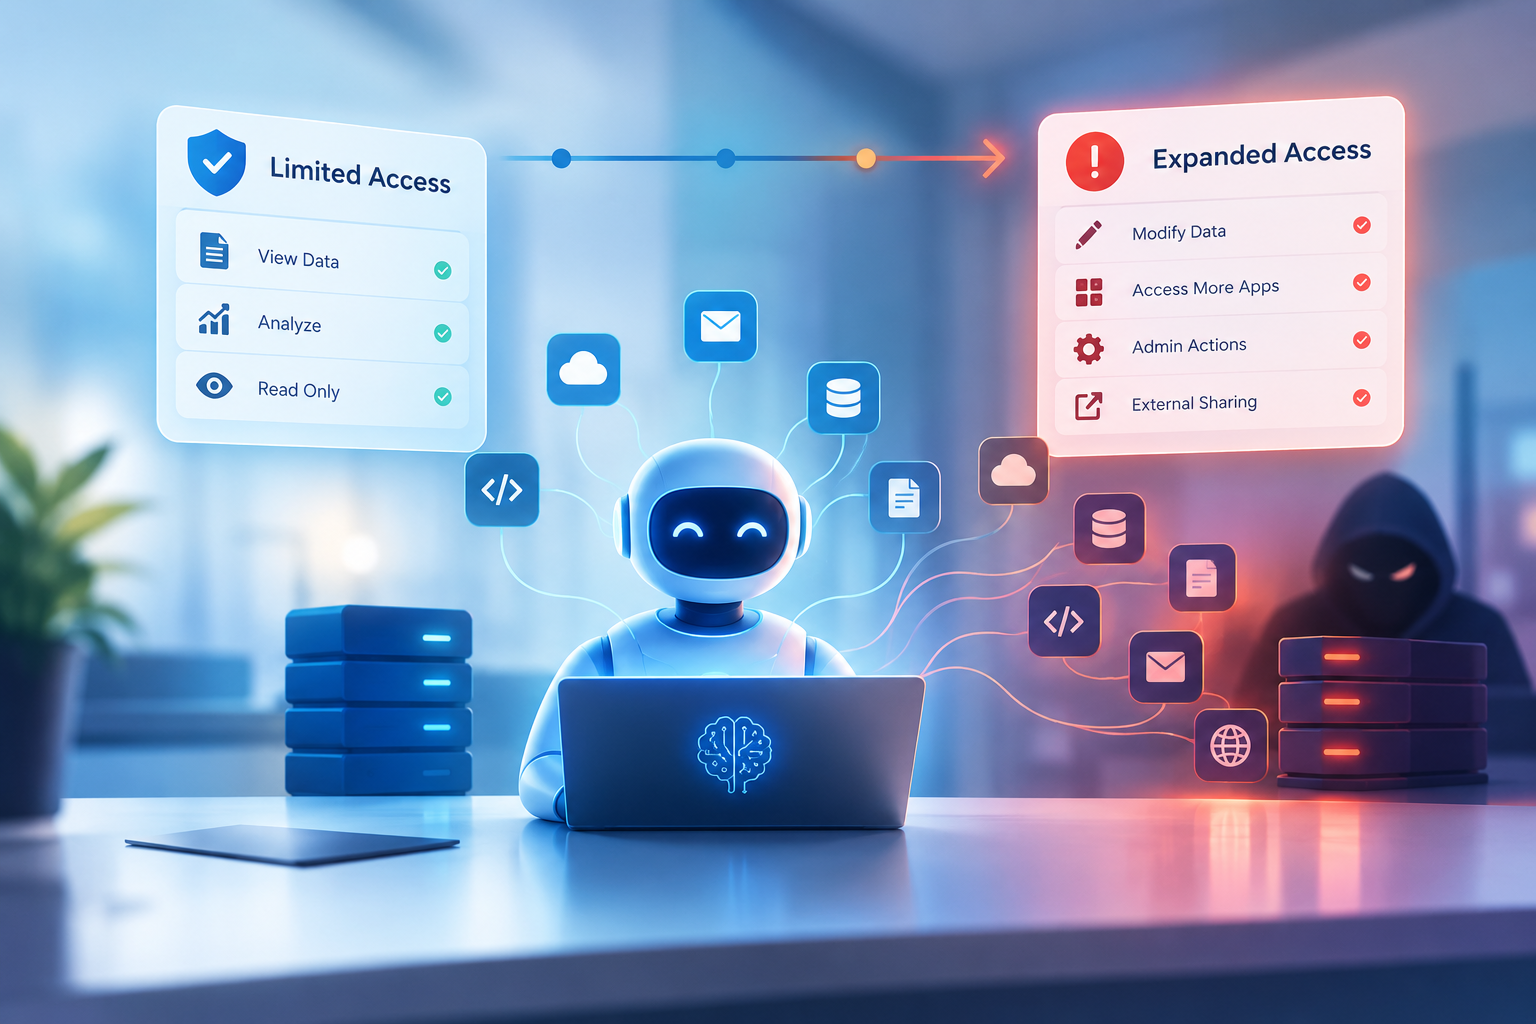
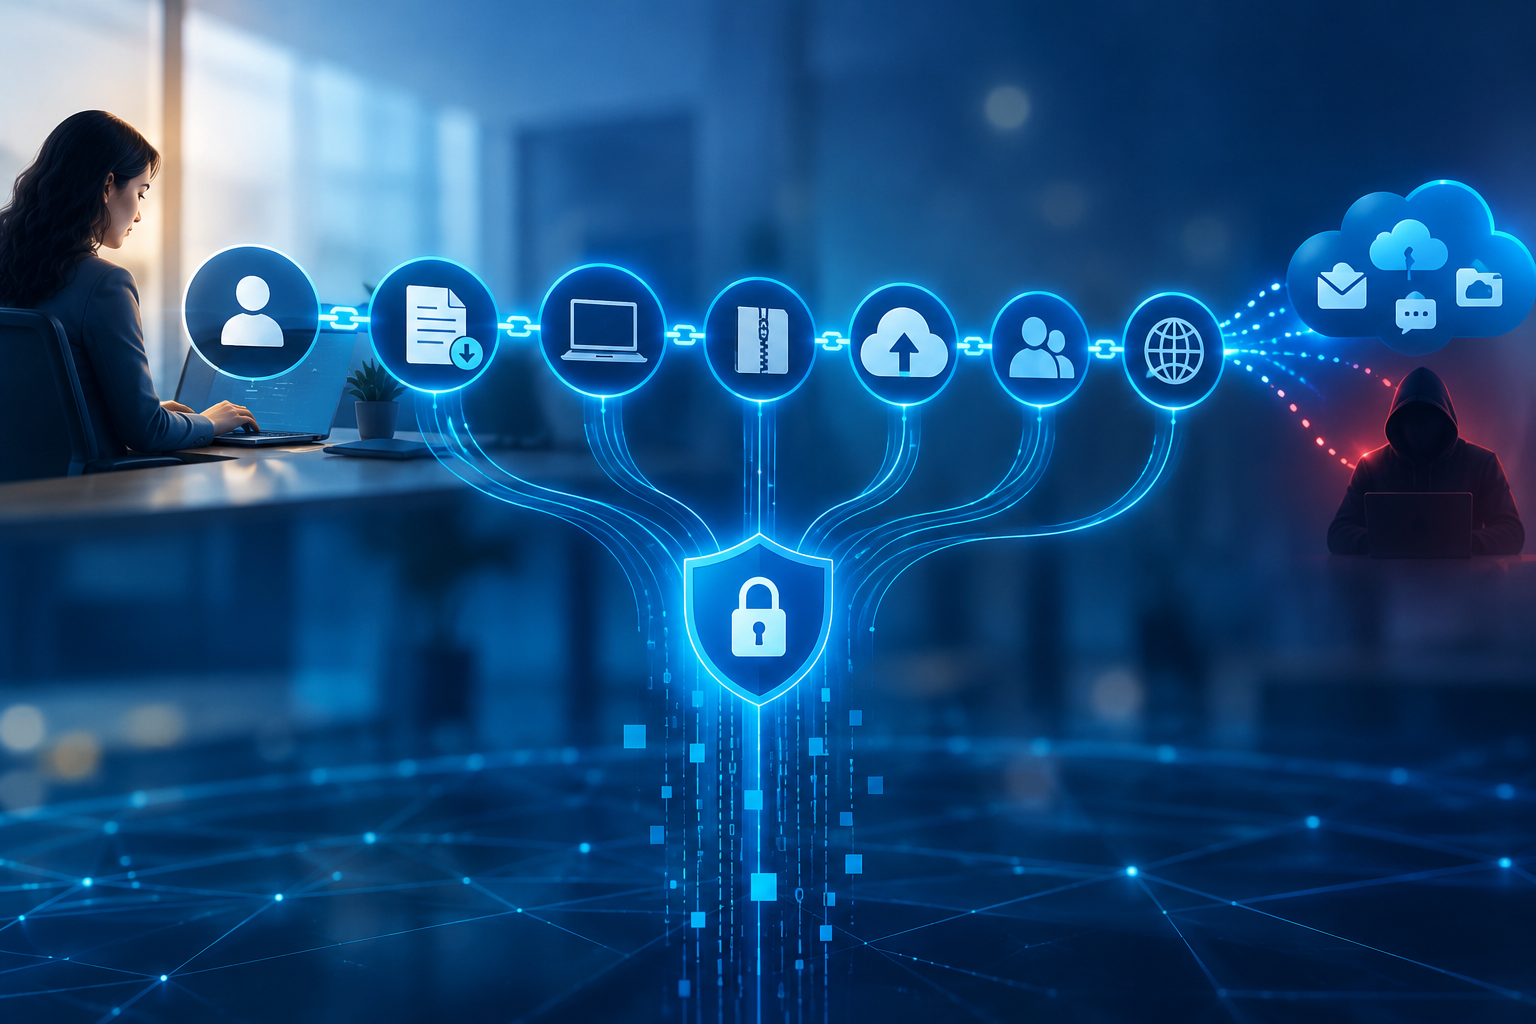
Behavioral Governance: The Next Frontier of AI Security For years, cybersecurity governance has focused on who can access what. Organizations built identity and access management programs, enforced least privilege, implemented Zero Trust, and regularly reviewed user permissions. But the digital environment is changing rapidly. With the rise of AI agents and autonomous systems, a new question is becoming equally important: What is the AI actually doing with the access it has? This is where Behavioral Governance is emerging as an important security concept. What Is Behavioral Governance? Behavioral Governance is the practice of continuously monitoring, evaluating, and controlling the actions and behavior of digital entities—particularly AI agents and other non-human identities—rather than relying only on their assigned permissions. An AI agent may have legitimate access to email, cloud storage, databases, APIs, or business applications. The security risk may not come from the permission itself, but from how that permission is used. For example, an AI agent authorized to access customer records may suddenly begin querying thousands of records, sending information to an unfamiliar system, or performing actions outside its normal business workflow. Traditional access reviews may show that the agent is properly authorized. Behavioral governance asks a different question: Was that behavior expected? Why Traditional Access Control Is No Longer Enough Traditional security controls generally establish boundaries around identity and access. But AI agents can operate dynamically. They may interpret instructions, interact with multiple systems, call APIs, generate content, initiate workflows, and make decisions based on changing context. This creates a new security challenge: An authorized identity can still behave in an unauthorized way. Behavioral governance therefore adds another layer of control by establishing a baseline for expected activity and identifying deviations from that baseline. What Should Organizations Monitor? A behavioral governance framework can monitor factors such as: • Which systems an AI agent interacts with • What data it accesses • Volume and frequency of requests • APIs and external services it invokes • Changes in normal operating patterns • Unexpected data movement • Unusual privilege usage • Actions performed outside approved workflows • Attempts to bypass established controls • Changes to the agent's instructions, tools, or configuration The objective is not simply to monitor activity. It is to understand whether the activity remains consistent with the agent's intended purpose. From “Least Privilege” to “Least Behavior” Least privilege remains an important security principle. However, in an agentic environment, organizations may need to complement least privilege with least behavior. An AI agent should not only have limited access—it should operate within clearly defined behavioral boundaries. For example: An agent may access a customer database, but it should not automatically export the entire database. An agent may create support tickets, but it should not modify security configurations. An agent may access financial information, but it should not transfer that information to an unapproved external service. These behavioral boundaries can help reduce the impact of compromised credentials, manipulated instructions, malicious prompts, or unintended AI actions. Behavioral Governance and Data Security The concept becomes particularly important for sensitive and regulated information. AI agents increasingly interact with: Customer Data → Financial Data → HR Data → Source Code → Business Documents → Security Logs Without behavioral monitoring, organizations may know that an AI system is authorized to access this information without knowing whether its actual usage remains appropriate. Behavioral governance can therefore support data loss prevention, privacy protection, incident detection, third-party risk management, and regulatory compliance. What Organizations Should Start Doing Organizations adopting AI agents should consider establishing: 1. AI Agent Inventory – Know which agents exist and what business purpose they serve. 2. Identity Mapping – Associate every agent with its identity, owner, permissions, and accountable business function. 3. Behavior Baselines – Define what normal activity looks like. 4. Continuous Monitoring – Detect unusual access, data movement, and system interactions. 5. Behavioral Policies – Define actions that are permitted, restricted, or prohibited. 6. Human Escalation – Require human approval for high-impact or sensitive actions. 7. Periodic Reviews – Reassess whether an agent's permissions and behavior still match its intended purpose. The Future of AI Security The next phase of cybersecurity will not be determined solely by how effectively organizations control access. It will also depend on how effectively they control behavior. As AI agents become part of everyday business operations, organizations may need to treat them less like passive software and more like active digital entities operating within the enterprise. The critical security question is therefore evolving: “Does this entity have permission?” to “Is this entity behaving as it is supposed to?” Behavioral Governance may become one of the key foundations for securing the increasingly autonomous digital enterprise.