
 Trupti Thakur
 #Cybersecurity #DataSecurity #IAM #ZeroTrust #AIGovernance #InformationSecurity #DataProtection #CyberRisk #CloudSecurity #LeastPrivilege #ISO27001 #IdentitySecurity #AI
The Five Minutes Identity
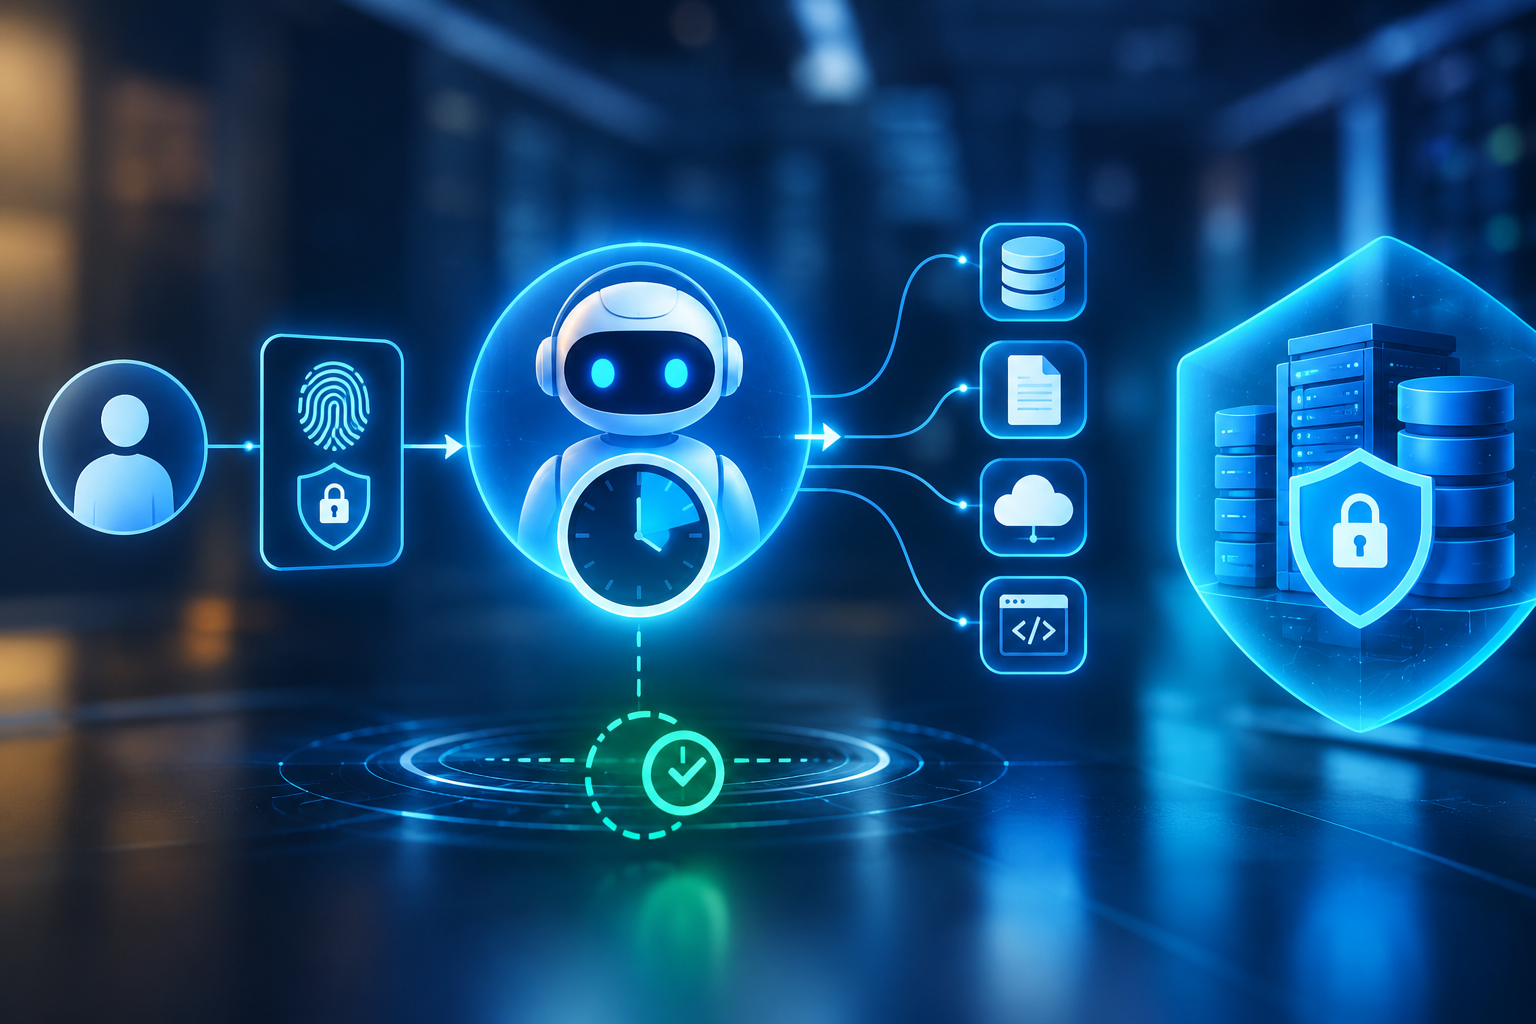
Absolutely. “The Five-Minute Identity” is a strong topic because it connects data security with one of the fastest-evolving areas of security: ephemeral identities and AI-agent access. NIST has recently highlighted that short-lived agents need equally short-lived, tightly scoped credentials and authorizations rather than traditional long-lived access. (NIST) The Five-Minute Identity: Securing Data in the Age of Ephemeral Access For decades, identity security has been built around a relatively simple assumption: identify the user, authenticate them, grant access, and periodically review their permissions. That model is being challenged. AI agents, automated workloads, cloud-native services, and short-lived applications can now exist for minutes—or even seconds—while accessing sensitive databases, APIs, documents, and business systems. NIST's recent work on AI-agent identity specifically raises the need to consider whether agent identities should be ephemeral and how their authorization should change with context. This creates a new security question: What happens when an identity exists only long enough to access your most valuable data? The Problem with Permanent Trust Traditional access management often relies on static accounts, persistent service credentials, and broad permissions. Even when these controls are periodically reviewed, the identity may remain active long after the original business requirement has changed. An ephemeral identity changes this model. Instead of granting an AI agent or workload permanent access, an organization can issue a short-lived identity with narrowly defined permissions, valid only for a specific task, resource, or transaction. The objective is simple: No task → No identity. No requirement → No access. Task completed → Identity expires. Why Five Minutes Can Be Safer Than Five Years Short-lived credentials can significantly reduce the window available for misuse if an identity is compromised. However, simply making credentials expire quickly is not enough. The identity must also be: • Uniquely identifiable • Tightly scoped • Bound to a specific purpose • Limited to necessary data and tools • Continuously monitored • Automatically revoked or expired • Traceable back to the initiating user, application, or business process NIST notes that AI agents should be treated as distinct entities with their own identifiers, credentials, and entitlements rather than simply sharing human credentials. (NIST) The New Data Security Challenge The bigger concern is not merely who accessed the data. It is: Why did they access it, what authority did they have, what other data did they combine with it, and where did the resulting information go? An AI agent may retrieve information from multiple systems, combine it, generate a new output, and pass that output to another service—creating a data trail that traditional access logs may not adequately explain. This makes identity, authorization, data lineage, and continuous monitoring increasingly interconnected. Moving Toward Just-in-Time Data Access The future of data security is therefore moving from “trust and periodically review” toward “authorize, observe, and expire.” Organizations should consider implementing: Just-in-time access + least privilege + short-lived credentials + contextual authorization + continuous monitoring. The goal is not to eliminate automation. It is to ensure that automation does not create permanent access pathways to sensitive information. The Five-Minute Security Mindset The most important question for modern data security may no longer be: “Who has access to this data?” It may become: “Who—or what—has access to this data right now, for what purpose, and for how long?” As AI agents and non-human identities become more common, identity itself is becoming temporary, contextual, and purpose-driven. The five-minute identity represents more than a technical control. It represents a shift in security philosophy: Trust should have an expiration date. This is where the future of Zero Trust, IAM, AI governance, and data security begins to converge.