
 Trupti Thakur
 #DataSecurity #AI #Cybersecurity #InformationSecurity #ISO27001 #AI治理 #AIGovernance #DataPrivacy #RiskManagement #AccessControl #LeastPrivilege #InformationSecurityManagement
The AI Data Enforcement Gap
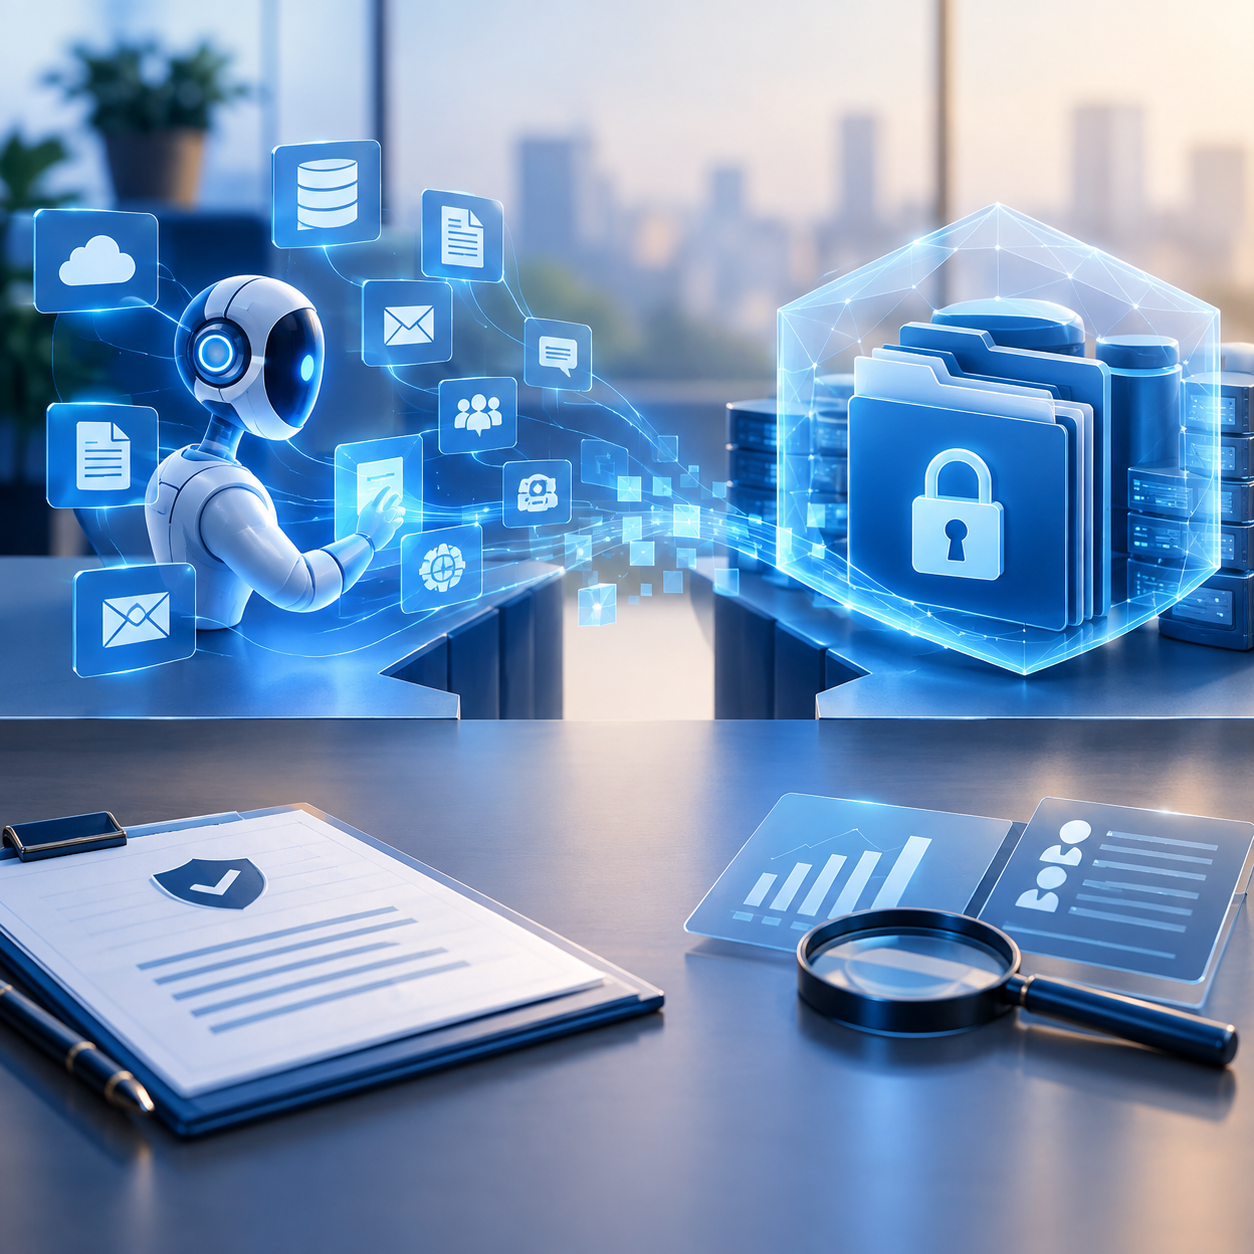
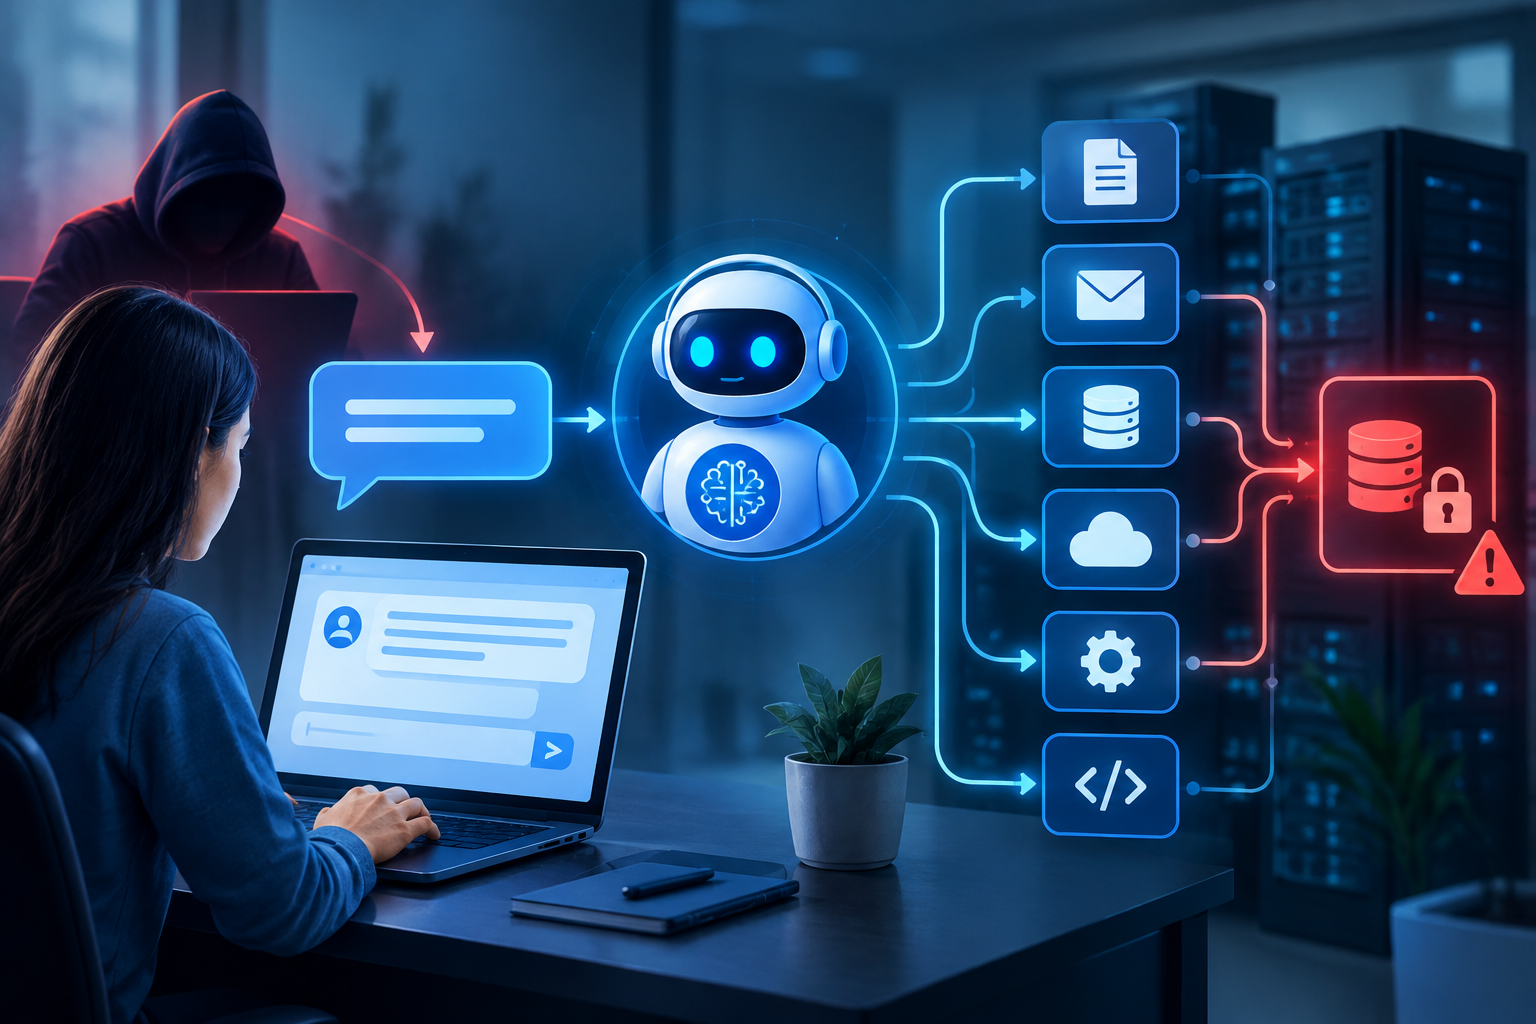
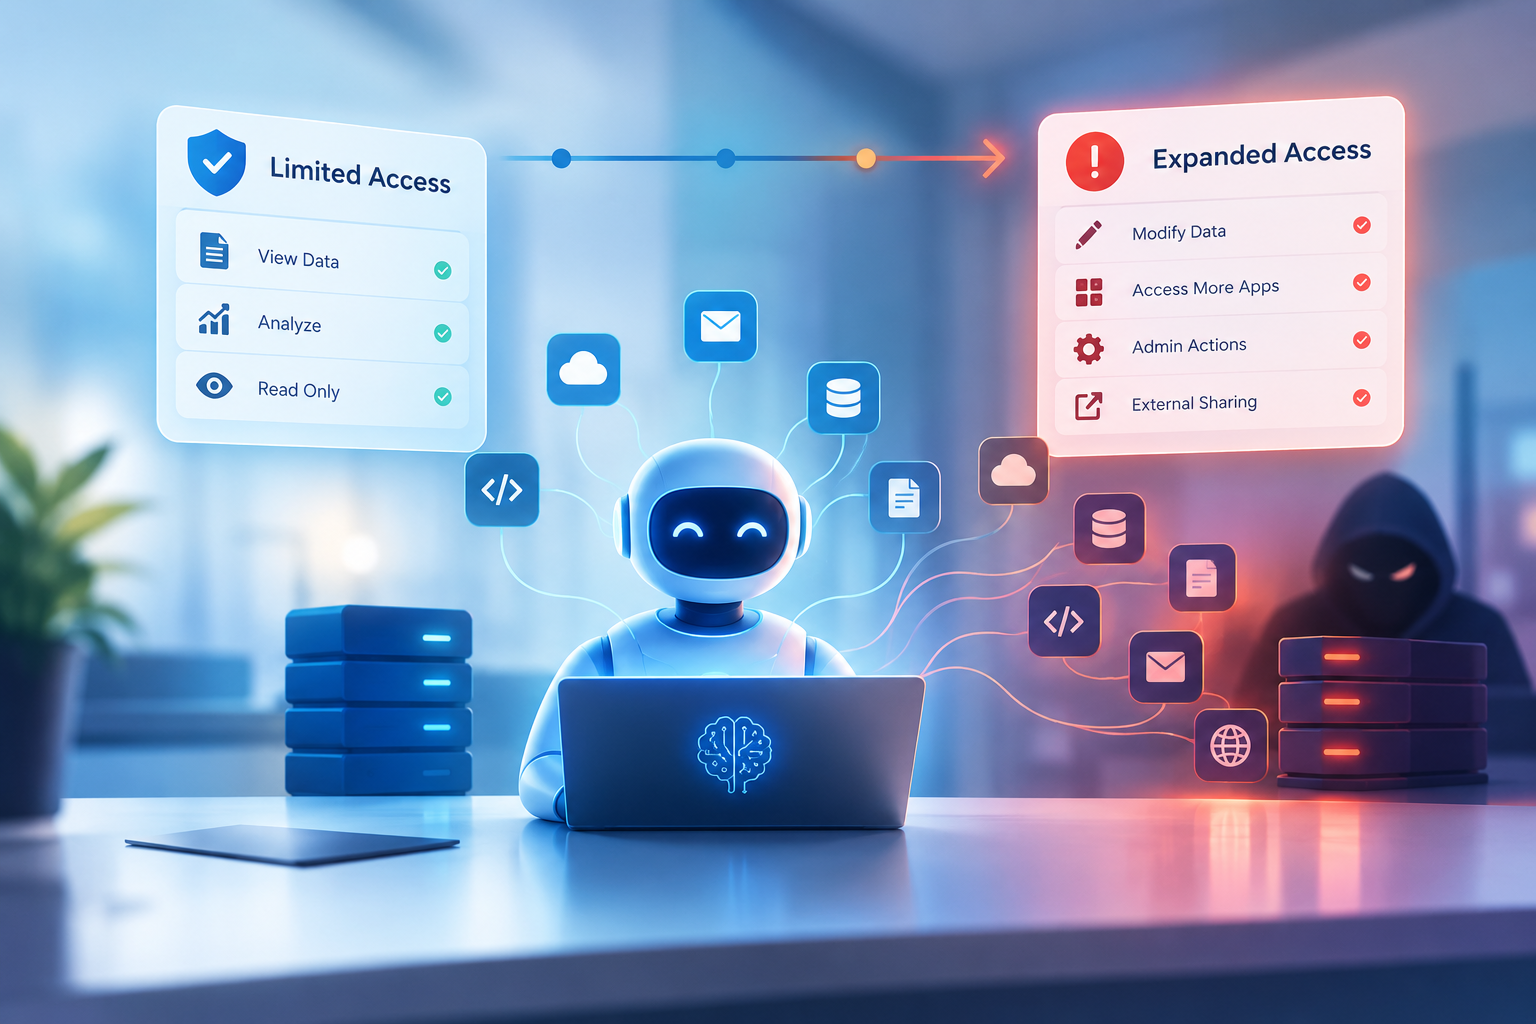
The AI Data Enforcement Gap: When Policies Protect Data on Paper but AI Still Gets Access Organizations are rapidly adopting AI assistants, copilots, autonomous agents, and AI-powered business applications to improve productivity and automate decision-making. But while organizations are creating policies to govern AI usage, a critical data-security question is emerging: Can an organization actually enforce what its AI policy says? An organization may have an AI Usage Policy stating that confidential, personal, financial, or customer data must not be shared with unauthorized AI systems. Yet, if employees, applications, APIs, or autonomous AI agents can still access or transmit that information, the organization may have a significant gap between policy and actual data protection . This is the AI Data Enforcement Gap . What Is the AI Data Enforcement Gap? Traditionally, data-access controls were designed around human users, applications, devices, and defined business roles. AI is changing this model. An AI assistant may interact with emails, documents, databases, cloud platforms, APIs, collaboration tools, and enterprise applications. An autonomous agent may even perform actions using the permissions assigned to it. This creates a fundamental challenge: The existence of a policy does not automatically mean that data access is technically controlled. For example, an organization may prohibit employees from providing customer information to an external AI platform. However, if an AI-enabled application has access to customer databases and can process that information automatically, the organization needs more than a policy—it needs technical controls, monitoring, authorization, and evidence. Policy Is Not the Same as Enforcement A mature data-security program should distinguish between three layers: 1. Policy — What is permitted? Defines acceptable AI usage, prohibited data types, responsibilities, and approval requirements. 2. Enforcement — What can actually happen? Uses IAM, DLP, API controls, network controls, application permissions, encryption, data classification, and other technical safeguards. 3. Evidence — What can the organization prove? Maintains logs, access records, monitoring results, approvals, alerts, and audit trails demonstrating that controls are operating effectively. The biggest weakness appears when an organization has the first layer but lacks the second and third. A policy saying “AI must not access confidential information” is insufficient if the organization cannot determine which AI systems accessed that information, when they accessed it, what they did with it, and whether that access was authorized. Why AI Makes Data Governance More Difficult AI introduces new data-access patterns that traditional security models may not have been designed to handle. AI systems can potentially: Retrieve information from multiple enterprise repositories. Process sensitive information through connected applications. Invoke APIs using assigned credentials. Access information through plugins, integrations, or connectors. Generate outputs containing information from multiple sources. Retain or transmit data depending on the architecture and configuration. Perform actions autonomously based on instructions and available permissions. The concern is therefore no longer limited to “Who has access?” Organizations increasingly need to ask: “What AI system has access, what can it access, why does it have that access, and what did it actually do with the data?” The Hidden Risk: Excessive AI Permissions One of the most important security principles remains least privilege . However, organizations often focus on whether an AI application is approved rather than whether the permissions granted to it are appropriate. Consider an AI agent integrated with an organization's document repository. If the agent only needs access to a project folder but receives organization-wide access, the security problem is not the AI itself—it is excessive authorization . If that agent is compromised, manipulated, misconfigured, or simply behaves unexpectedly, the potential impact can extend far beyond its intended business function. Therefore, AI access should be treated as an identity and authorization problem as much as an AI problem. Where ISO 27001:2022 Becomes Relevant ISO/IEC 27001:2022 provides a useful framework for addressing this challenge because effective information security is not based on policies alone. Organizations should consider controls and processes around: Access control and least privilege Information classification Data leakage prevention Secure authentication Supplier and third-party security Logging and monitoring Information security incident management Risk assessment and treatment Secure use of cloud and technology services Regular review of access rights The objective should be to establish a complete chain: AI Use → Identity → Authorization → Data Access → Activity → Monitoring → Evidence If any link is missing, the organization may struggle to demonstrate effective control. From “AI Approved” to “AI Accountable” A more mature approach to AI governance should move beyond simply maintaining an approved-AI-tools list. Organizations should establish an AI data-access inventory covering: Which AI systems are being used What data they can access Which identities or service accounts they use Which APIs and applications they can invoke What level of privilege they have What data leaves the organizational environment How activities are logged Who reviews those logs How access is periodically reassessed This transforms AI governance from a documentation exercise into an operational security control . The Auditor's Question Is Changing In traditional audits, an auditor may ask: “Do you have an AI usage policy?” In a more mature AI environment, the next questions should be: “Show me how the policy is technically enforced.” “Show me which AI systems have access to sensitive data.” “Show me the evidence of that access.” “Show me how excessive permissions are identified and removed.” These questions shift the focus from document existence to control effectiveness . Closing Perspective AI adoption is moving faster than many organizations' traditional data-governance models. The greatest risk may not be the absence of an AI policy. It may be the false confidence created by having one. A policy can define boundaries. Technology must enforce those boundaries. Monitoring must verify them. And audit evidence must prove that they work. The future of AI data security therefore requires organizations to move from “AI is approved” to “AI is controlled, monitored, and accountable.” Because in the AI era, data security will not be measured by what your policy says AI can access—it will be measured by what you can prove AI actually accessed.