
 TRUPTI THAKUR
 #DPDPAct #ArtificialIntelligence #AIPrivacy #DataProtection #InformationSecurity #ISO27001 #ISO42001 #CyberSecurity #PrivacyCompliance #AIGovernance #DataPrivacy #ResponsibleAI
When DPDP Meets AI
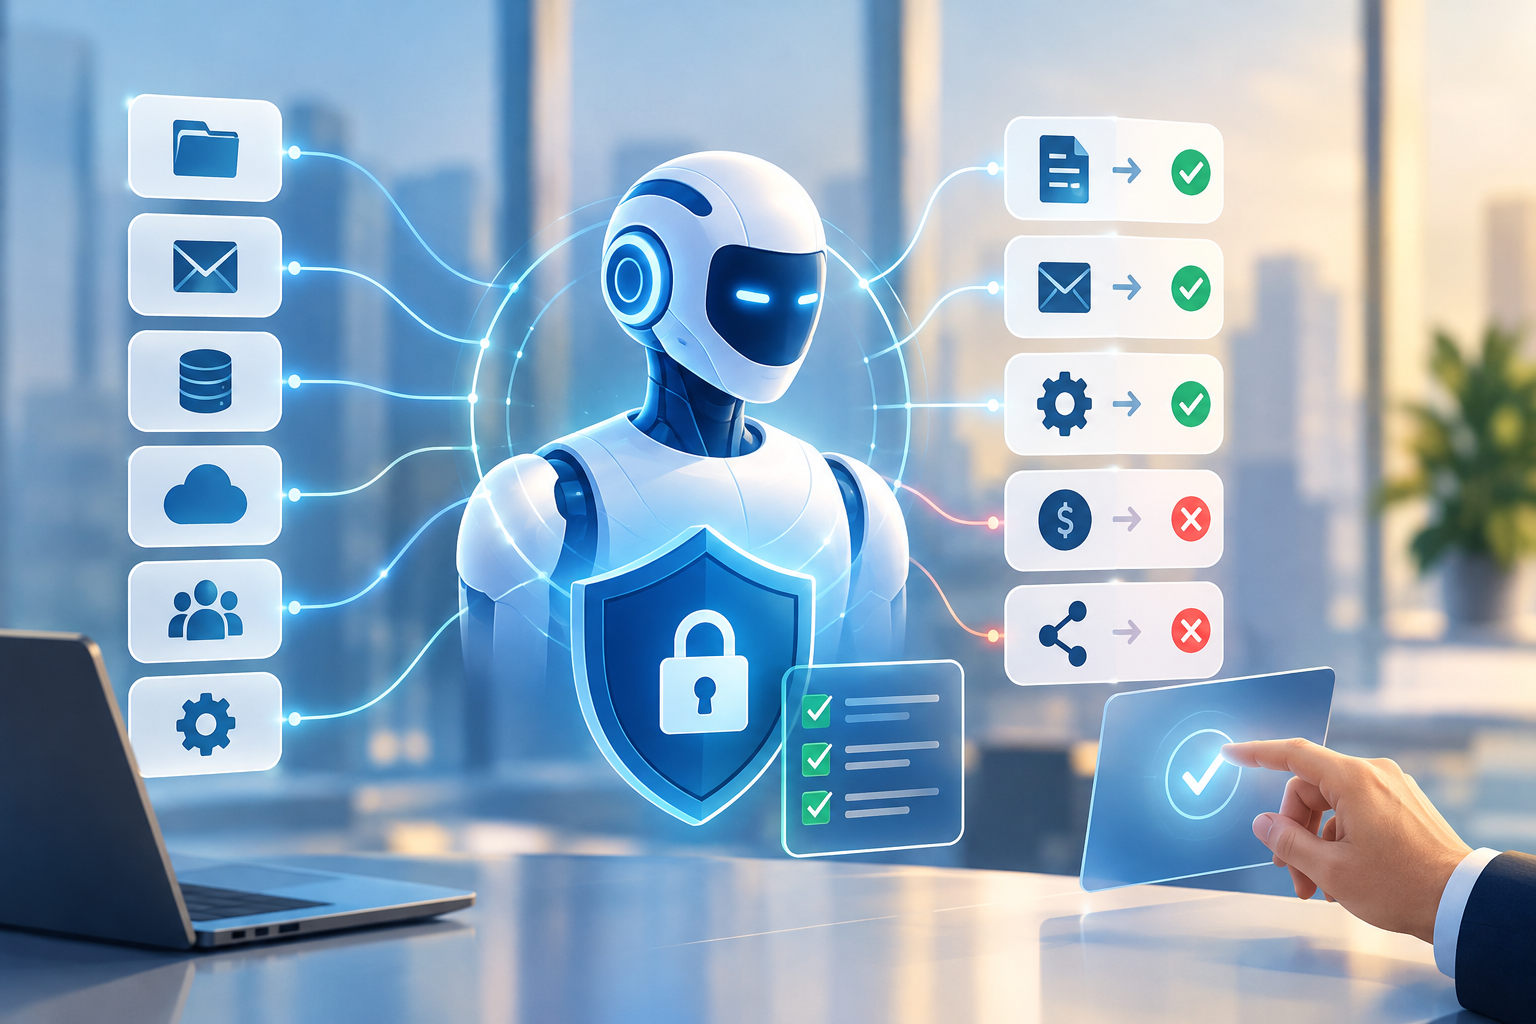
Artificial Intelligence is transforming how organizations collect, process, analyze and utilize information. From AI-powered customer support and automated decision-making to predictive analytics and personalized services, organizations increasingly rely on personal data to make AI systems more effective. However, this growing dependence on data introduces an important question: How can organizations innovate with AI while ensuring that personal data remains protected? India's Digital Personal Data Protection (DPDP) Act, 2023, brings a stronger focus on accountability, lawful processing and the protection of digital personal data. As organizations adopt AI-driven technologies, aligning AI practices with data protection obligations is becoming an important governance challenge. The Hidden Privacy Risks Behind AI Systems AI systems often process large volumes of information during development, training, testing and deployment. Personal data may enter these systems through customer interactions, employee records, uploaded documents, application databases and third-party integrations. Some key privacy risks include: Unintended Data Exposure: Employees may upload confidential customer or organizational information into publicly accessible AI platforms. Excessive Data Collection: AI models may process more personal information than necessary for their intended purpose. Data Retention Challenges: Personal information may remain within datasets, logs, backups or AI-related storage environments even after its original purpose has been fulfilled. Third-Party AI Dependencies: External AI service providers may introduce additional risks concerning data processing, storage, access and security. Limited Transparency: Organizations may struggle to identify how personal data is being used across AI workflows and integrated applications. These challenges highlight that AI security is not limited to protecting the technology itself; it also requires controlling how personal data enters, moves through and is retained within AI environments. DPDP Act: Bringing Accountability to AI-Driven Data Processing The DPDP Act establishes obligations for Data Fiduciaries concerning the processing of digital personal data. Organizations must ensure that personal data is processed for lawful purposes, with appropriate notice and consent where applicable, and that reasonable security safeguards are implemented. When AI systems are involved, these responsibilities become particularly important. Organizations should consider the following measures: Purpose-Based Data Processing: Ensure that personal data used in AI applications is aligned with the specified purpose and applicable legal requirements. Data Minimization: Avoid feeding unnecessary personal or sensitive business information into AI systems. Access Governance: Restrict access to AI platforms, datasets and training environments based on business requirements. Data Retention and Deletion: Establish appropriate retention and deletion practices for personal data across AI-related environments, subject to applicable legal requirements. Vendor and Third-Party Assessment: Evaluate AI service providers, their data handling practices, contractual obligations and security safeguards. Incident Management: Establish procedures to identify, investigate and respond to unauthorized access, disclosure or other personal data breaches. It is important to recognize that the DPDP Act does not prohibit the use of AI. Instead, organizations must ensure that their AI-related data processing complies with applicable data protection obligations. Connecting AI Governance with ISO/IEC 27001 and ISO/IEC 42001 DPDP compliance and information security management should not operate as separate initiatives. Organizations can strengthen their approach by integrating data protection requirements into their existing management systems. ISO/IEC 27001:2022 provides a structured framework for managing information security risks, including access control, information classification, supplier security and incident management. Similarly, ISO/IEC 42001:2023 provides a management system framework for responsible AI governance, addressing risks associated with the development and use of AI systems. Together, these frameworks can help organizations establish a more comprehensive governance approach by connecting information security, privacy protection, AI risk management and organizational accountability. What Organizations Should Do Next Organizations should move beyond simply approving AI tools and establish clear governance over how those tools process information. A practical approach includes: Maintaining an inventory of approved AI applications and their data-processing activities. Conducting privacy and security risk assessments before introducing AI solutions. Establishing an AI usage policy defining permitted and prohibited data sharing. Implementing employee awareness programmes on responsible AI usage. Reviewing AI vendors and third-party data-processing arrangements. Periodically monitoring AI environments for unauthorized data exposure and access. Conclusion AI innovation and personal data protection must progress together. As organizations increasingly integrate AI into their business operations, the challenge is no longer simply about controlling access to information; it is about understanding how information is collected, processed, reused, retained and protected throughout the AI lifecycle. The DPDP Act provides an important foundation for personal data protection, while ISO/IEC 27001 and ISO/IEC 42001 offer structured approaches to information security and AI governance. The future of responsible AI will not be determined by how much data an organization can process, but by how responsibly it can manage and protect that data.